New CIC Privacy Rules Are Here: How DGX HRMS Role Permission System Helps Sites Protect Worker Data
Facing the Construction Industry Council's strict privacy requirements for worker records, how can project owners and PMs use DGX HRMS's hybrid strategy-and-role architecture to finely control data access, ensure compliance, and avoid legal liability? This article takes a deep dive.
Time & Payroll Suite
Attendance, Payroll and Access Control Solution for Cost Reduction and Productivity Gains Details
All‑in‑one automated timekeeping and payroll system with robust, secure processes to guarantee payroll integrity. Includes leave management, shift rostering, multi‑site and chain support, multi‑ledger accounting, and comprehensive modules.
How Can You Use the DGX HRMS Role Permission System to Protect Worker Data Under CIC Privacy Requirements?
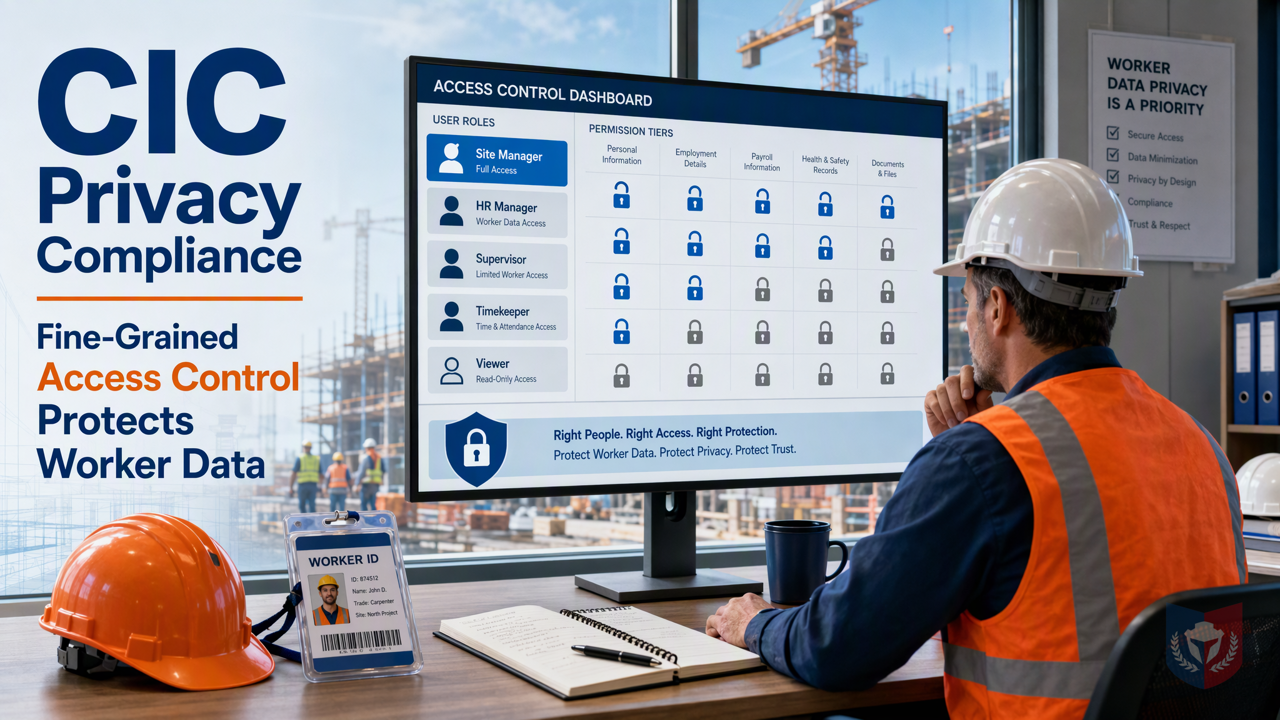
The Construction Industry Council (CIC) and the Development Bureau of Hong Kong have been actively promoting the digital management of site safety and subcontractor registration in recent years, with increasingly strict privacy requirements for worker records. According to CIC regulations, after a worker leaves employment, site management personnel must update the "end date" in the worker registration form in the CWRG system within a grace period (generally 7 days), rather than directly deleting historical records, and simultaneously disable their site permissions to ensure they can no longer clock in. Failure to handle this on time may constitute an infringement of worker privacy, and the project responsible person and project manager (PM) must bear legal responsibility.
Faced with such compliance challenges, an HRMS system with fine-grained permission control is essential. The DGX HRMS attendance and payroll management system has a built-in "policy and role hybrid architecture" that helps site management effectively protect worker data while meeting CIC privacy requirements. This article will explain from a practical perspective how DGX HRMS, through its role permission system, lets you rest easy on the path to compliance.
1. CIC Privacy Requirements and Site Management Pain Points
CIC's privacy protection for worker data is mainly reflected in the Construction Workers Registration Ordinance and related guidelines. The main contractor must submit daily attendance records (DAR) on time and properly handle workers' registration records when they leave employment. In practice, sites are often operated by multiple management personnel, and if permissions are not clearly divided, problems such as mistakenly deleting data, failing to update on time, or unauthorized access are likely to occur, increasing legal risk.
In addition, the site environment is complex and personnel turnover is frequent. Manual permission management is not only time-consuming but also prone to errors. Therefore, a system that can finely configure permissions according to job responsibilities becomes the key to compliance management.
2. Core Design of the DGX HRMS Role Permission System
DGX HRMS's permission management adopts a "policy and role hybrid architecture," combining flexibility and rigor. The system presets multiple roles and can customize them according to business operations. The following is the role division under general circumstances:
- System Administrator SystemAdmin: Has the highest permissions and is responsible for overall system configuration and maintenance.
- Company Administrator Admin: Manages company-level users and permissions and can review company services.
- Company Operator MainComOperator: Performs daily attendance and payroll operations, such as batch importing attendance lists and handling scheduling.
Design and Architecture Philosophy
The core idea of the hybrid architecture is that "roles grant basic capabilities, and policies control detailed behavior." Roles define the types of operations users can perform (such as view, edit, and approve), while policies further limit the data scope (such as only viewing worker data for the site they belong to). This design simplifies permission assignment while enabling fine-grained control, ensuring that sensitive data is accessible only to authorized personnel.
Configuring Permissions and Roles
Administrators can assign roles to each user through the "User Role Authorization" function in the system management module. The system provides a "Role Definition List" that clearly displays the default permissions of each role. When necessary, the permission combination of a specific role can be adjusted through "Role Authorization," or custom roles can be created to meet special needs.
For example, for a site PM, the "Company Operator MainComOperator" role can be granted, paired with policies restricting them to only viewing and updating worker records for the site they belong to, and prohibiting deletion of historical records, allowing only updates to the "end date." In this way, even if the PM operates frequently, they will not accidentally cross the privacy red line.
Scenarios Requiring Both Specific Roles and Permissions
Some operations require both a specific role and permission to execute. For example, when approving payroll adjustments, the user must have the "approve" permission and be granted the corresponding role. The "Company Service Review" function in system management reflects this principle, ensuring that important operations are properly authorized.
3. System Management Functions Support Compliance
The DGX HRMS system management module provides multiple functions to help sites maintain compliance:
- User Role Authorization: Flexibly assign roles and update them immediately as positions change.
- Role Definition List: Default roles are clear at a glance, making management easier.
- Role Authorization: Finely adjust role permissions to implement the principle of least privilege.
- Company Service Review: Ensure service changes are approved and meet internal control requirements.
- Configuration ./CONFIG: System parameter settings that can be adjusted according to company policy.
- Multi-language Management: Supports a multi-language interface for ease of use by people from different backgrounds.
- System Users: Centrally manage user accounts for easy enabling or disabling.
- Batch Import Attendance List: Quickly import worker lists to reduce manual errors.
Through these functions, sites can establish a clear permission system to ensure that worker data is used only within the authorized scope.
4. Report Monitoring and Compliance Auditing
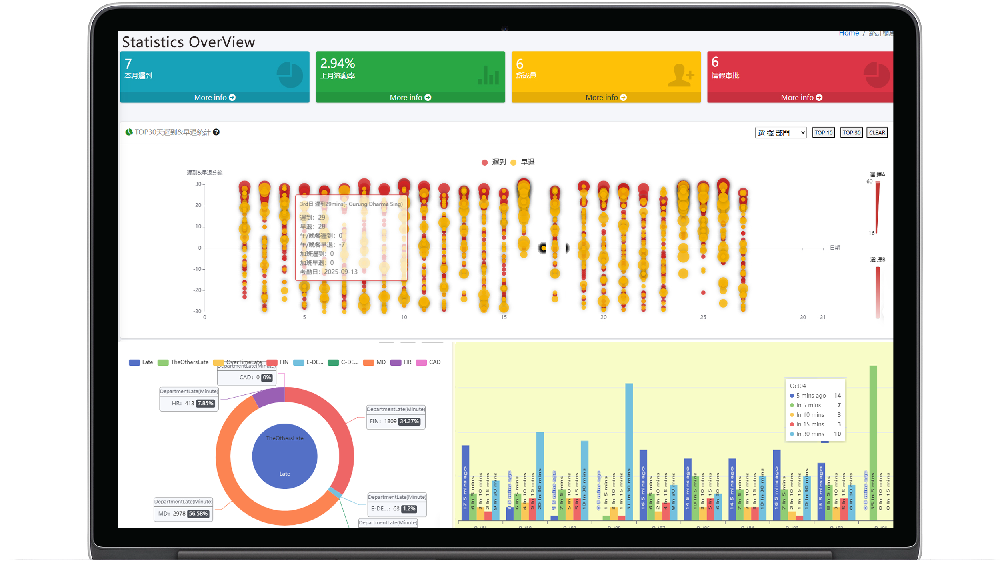
DGX HRMS's reporting function can produce various attendance and payroll reports, and management can regularly review access records of worker data to promptly detect abnormal operations. For example, reports can be used to confirm whether the "end date" of departed workers has been updated and whether permissions have been disabled, ensuring compliance with CIC's 7-day processing requirement.
5. Practical Scenario: Departing Worker Processing Workflow
Suppose worker Chan Tai Man leaves employment. The site PM needs to perform the following steps to meet CIC privacy requirements:
- Update End Date: In the CWRG system, set the "end date" of Chan Tai Man's registration record to the departure date rather than deleting the file.
- Disable Permissions: Disable their site permissions in DGX HRMS to ensure they can no longer clock in.
- Handle Payroll Settlement: If payroll calculation is involved, add an "account detail" through the system and note "payroll 7-day notice pay," then confirm the deduction through the approval process, and finally complete the bank transfer and report archiving.
DGX HRMS's permission system ensures that only authorized personnel (such as the Company Administrator Admin) can perform the above sensitive operations, and all actions are recorded for auditing.
6. Conclusion
CIC's privacy requirements for worker data will only become stricter, and site management must rely on a reliable system to implement compliance. DGX HRMS's role permission system, through its policy and role hybrid architecture, achieves fine-grained control, not only protecting worker data but also reducing legal risk. Whether you are a system administrator, company administrator, or operator, you can work efficiently within a clear permission framework. Adopt DGX HRMS today and make compliance your competitive advantage.
Featured Reviews
No reviews yet. Be the first to leave one.
Write a review
Supports bold and lists; do not paste external scripts or images
0 / 2000
Visible after review